- Need Technical Assistance? events@securityweek.com

This summit is laser-focused on the next generation of Zero Trust and Identity security, moving beyond theory to deliver actionable strategies for a world where every user, device, and workload must be explicitly verified. We will explore how to build a unified security framework by converging Zero Trust with SASE, leveraging AI to predict and defend against identity-based threats, and navigating the complex landscape of regulatory compliance to build a truly resilient organization.
Registered Attendees
Live Sessions
Technical Demos
Interactive Expo Hall
Resource Center
Attendees can expect to learn about:
Zero Trust Frameworks: Implementing Zero Trust principles across diverse and complex hybrid and multi-cloud environments.
AI-Powered Identity: The central role of AI and machine learning in analyzing user behavior, detecting anomalies, and mitigating advanced identity-based threats.
UX vs. Security: Balancing a frictionless user experience and the rise of Shadow IT with robust, continuous authentication.
Compliance & Governance: Aligning Zero Trust architectures with evolving data privacy regulations and security frameworks like NIST and CMMC.
ZTNA & SASE: Integrating Zero Trust Network Access (ZTNA) into a broader Secure Access Service Edge (SASE) architecture for a unified defense.
SecurityWeek Virtual Events Provide

Attackers used to have to hack in. Then the SaaS era taught them it was easier to log in.
Today, in the AI era, they barely need to try as employees are pasting customer data, credentials, and source code directly into AI tools, one prompt at a time. A single misconfigured permission or a careless copy-paste can expose data you can’t pull back.
Banning AI doesn’t work. It hurts productivity and pushes AI usage underground to personal accounts and unmanaged devices, where visibility drops to zero, and enforcement can’t be verified without observability.
This session makes the case for a different goal: how to enable secure usage instead of blocking access, and extend zero-trust principles to how humans and machines interact with AI.
Attendees will learn how to:
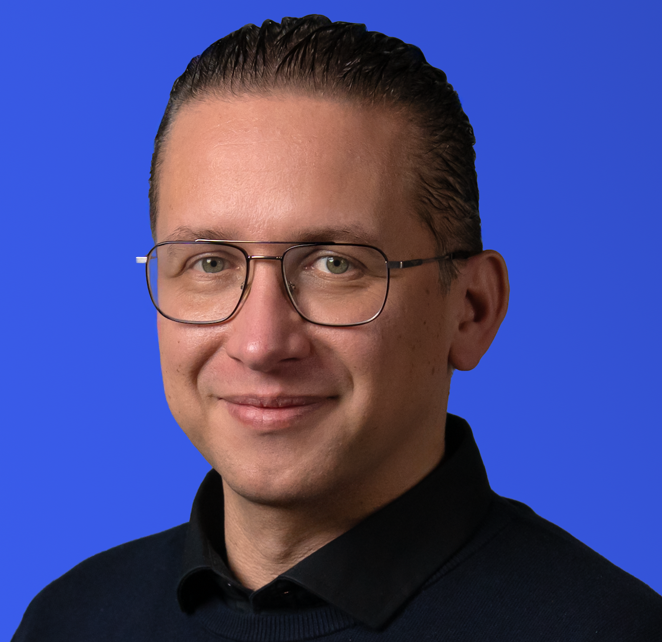
Andrius Buinovskis
VP Product Strategy
NordLayer
NIST wrote continuous, behavioral verification into the definition of Zero Trust in 2020: Access decisions should account for behavioral and environmental attributes, not just identity and device posture. Five years later, most implementations still verify once, at the point of access, and call that Zero Trust. ClearVector's 2026 Identity Intelligence Report shows what that gap actually looks like in production: 91% of identities running there are non-human, and the adversary increasingly relies on stolen but valid credentials that clear the same checkpoint as legitimate ones, moving undetected because nothing after login tells the two apart. AI widens the gap further, since an agent that inherits a developer's already-verified session can act for hours without ever being re-checked. John Laliberte, CEO of ClearVector, walks through where Zero Trust's own founding principle stops being practiced, using a real production incident as the anchor, and what it takes to build a pattern of life for an identity so verification never actually stops.
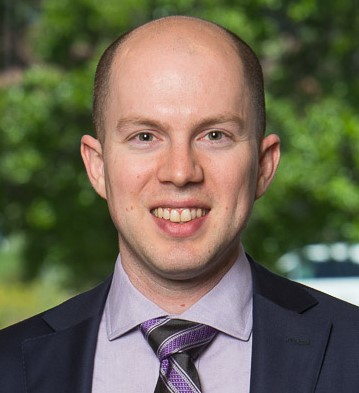
John Laliberte
CEO and Founder
ClearVector
Organized attackers aren’t breaking in, they’re becoming part of your extended workforce. AI-powered impersonation, deepfakes, hiring fraud, and MFA fatigue attacks now target corporate employees, frontline workers, contractors, and partners—across onboarding, access, and helpdesk workflows. As organizations expand across hybrid work and third-party ecosystems, identity has become the most exploited, and least consistently verified, attack surface. The problem? Most organizations still rely on implicit trust, assuming identities are legitimate after a single check, while attackers continuously impersonate, infiltrate, and escalate. According to IDC, over 80% of breaches are identity-driven, and organizations that adopt continuous, contextual identity verification achieve up to 43% reduction in fraud loss and 47% faster onboarding.
Curtis Muir
Sr. Director, Sales Engineering
Ping Identity
Stuart Proffitt
Sr. Director, Workforce Strategy
Ping Identity
We’re now taking a break!
Take this opportunity to visit the Exhibit Hall and explore our sponsors’ resources, solutions, and latest insights. Their subject matter experts are available now and ready to answer your questions and connect with you. Be sure to stop by before the next session begins!
AI is changing the role of identity across the enterprise. Human users are no longer the only actors interacting with sensitive systems and data — AI agents, copilots, APIs, and autonomous workflows are introducing new layers of access, intent, and interconnected risk.
In this session, we’ll explore why identity has become foundational to understanding AI risk, how AI changes traditional assumptions around access and trust, and what new attack paths emerge across connected systems. We’ll cover real-world scenarios involving intent, lateral movement, and overprivileged access, along with a practical framework for thinking about identity in the era of AI — and where organizations should begin.
Omer Mesika
Product Marketing Manager
Wiz